AI-Era Web Hacking: From Linux Basics to Your First Pentest Job
A live 8-week intensive: Linux, networking and web hacking, built for the AI era.
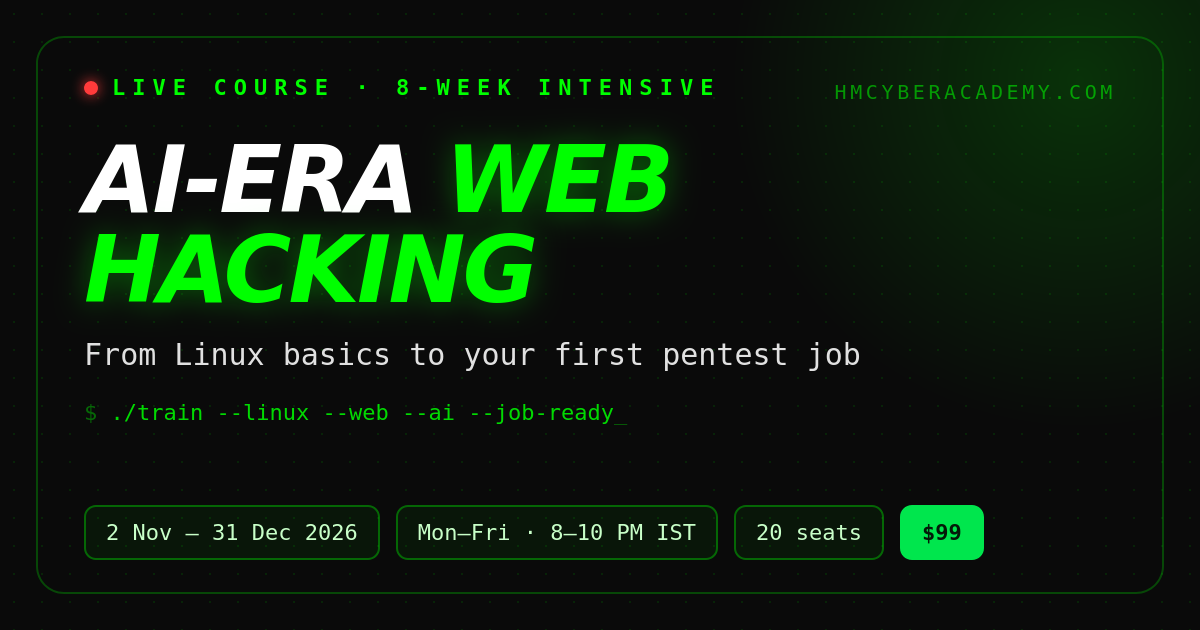
About this course
A live, hands-on path from Linux basics to your first web pentesting job, built for how security work is done today: with AI as your assistant, and AI features as a new attack surface.
Every class is taught live on Discord, Monday to Friday, 8–10 PM IST. Missed one? The recording is added to your classroom after the class.
What you get
- 44 live classes on Discord (88 hours), with a recording of every class
- Networking and Linux foundations with 30+ hands-on Linux labs
- Web hacking from SQL injection to request smuggling, with PDF walkthroughs and cheatsheets
- API security and AI-era hacking: using AI safely in pentests, and attacking AI features
- A capstone assessment with a reviewed report for your portfolio
- Resume preparation, an interview question bank, mock interviews and referrals within my network
- Private Discord and Telegram groups for doubts and updates
- Lifetime access to materials and recordings
Who it's for
- Beginners and intermediates aiming for VAPT and pentesting roles
- Students and working professionals who can give 2 hours on weekday evenings
- No prior hacking experience needed: basic computer skills are enough
Syllabus
44 live classes · Mon–Fri01 Week 1 · Foundations & Linux
- Mon 2 NovOrientation, lab architecture & rules of engagement: scoping, authorization, operating safely with AI assistants
- Tue 3 NovNetwork foundations for offensive security: TCP/IP, DNS, TLS 1.3, HTTP/1.1, HTTP/2 & HTTP/3
- Wed 4 NovLinux internals & the command line: filesystem, permissions, SUID & capabilities, processes, services
- Thu 5 NovOffensive Linux & shell craft: scripting, text processing, automation, tooling setup
- Fri 6 NovGuided Linux labs: enumeration, privilege & filesystem drills
02 Week 2 · Web Foundations & Reconnaissance
- Mon 9 NovHTTP protocol deep dive: state, sessions, caching semantics, header & encoding behavior
- Tue 10 NovThe modern web attack surface: SPAs, REST & GraphQL APIs, microservices, cloud edge & CDNs
- Wed 11 NovAttack-surface mapping & asset discovery: subdomain, content & parameter discovery
- Thu 12 NovClient-side reconnaissance: JavaScript analysis, source maps, hidden & undocumented endpoints
- Fri 13 NovInterception workflow & a repeatable, evidence-driven testing methodology
03 Week 3 · Server-Side Exploitation I
- Mon 16 NovAdvanced SQL injection: blind, time-based, out-of-band, second-order & filter evasion
- Tue 17 NovNoSQL, ORM & query-language injection
- Wed 18 NovOS command & argument injection: blind and chained execution
- Thu 19 NovPath traversal, LFI/RFI & file-handling abuse
- Fri 20 NovUnrestricted file upload to code execution: content-type, polyglot & parser confusion
04 Week 4 · Server-Side Exploitation II
- Mon 23 NovServer-side request forgery (SSRF): blind SSRF, cloud metadata & internal pivoting
- Tue 24 NovXML external entities (XXE) & insecure deserialization: object injection to RCE
- Wed 25 NovServer-side template injection (SSTI): sandbox escapes to RCE
- Thu 26 NovAuthentication & session attacks: fixation, token prediction, MFA weaknesses
- Fri 27 NovBroken access control & business-logic flaws: IDOR, broken function-level authorization, workflow abuse
05 Week 5 · Client-Side Exploitation
- Mon 30 NovCross-site scripting: reflected, stored & context-aware payload construction
- Tue 1 DecDOM-based XSS & DOM clobbering: source/sink analysis in modern frameworks
- Wed 2 DecCSRF, CORS misconfiguration & SameSite bypass
- Thu 3 DecClickjacking, UI redressing & cross-origin leaks (XS-Leaks)
- Fri 4 DecClient-side prototype pollution & browser-side supply-chain risks
06 Week 6 · Advanced Exploitation & AI I
- Mon 7 DecWeb cache poisoning & cache deception
- Tue 8 DecHTTP request smuggling (CL.TE / TE.CL) & HTTP/2 desync
- Wed 9 DecHTTP Host header & routing-based attacks
- Thu 10 DecOAuth 2.0 / OIDC & JWT exploitation: flow abuse, key confusion, token forgery
- Fri 11 DecGraphQL & REST API exploitation: introspection abuse, batching & authorization gaps (OWASP API Security Top 10)
07 Week 7 · Advanced Exploitation & AI II
- Mon 14 DecServer-side prototype pollution & gadget-chain exploitation
- Tue 15 DecRace conditions & concurrency flaws: limit-overrun & multi-endpoint
- Wed 16 DecAI-augmented offensive testing: LLM-driven recon, analysis & payload synthesis, with verification and opsec
- Thu 17 DecAttacking LLM-powered applications I: prompt injection (direct & indirect) & insecure output handling
- Fri 18 DecAttacking LLM-powered applications II: excessive agency, tool-call abuse & data/model leakage (OWASP LLM Top 10)
08 Week 8 · Job-Ready
- Mon 21 DecProfessional reporting & risk communication: CVSS, evidence, executive & technical narratives
- Tue 22 DecCapstone engagement kickoff: scoping & testing a deliberately vulnerable application
- Wed 23 DecCapstone working session: full-chain exploitation (+ optional offensive automation with Python & nuclei)
- Thu 24 DecCapstone debrief & mentor-reviewed report for your portfolio
- Fri 25 DecCareer launch: resume, LinkedIn, GitHub portfolio & interview question bank
09 Wrap-up
- Mon 28 DecCapstone demonstrations & peer review
- Tue 29 DecMock technical interviews I
- Wed 30 DecMock technical interviews II & doubt clearing
- Thu 31 DecGraduation: certification roadmap (eJPT, PNPT/BSCP, OSWE/OSCP), referrals & next steps
How enrollment works
- 1Click Enroll and sign in with your Google account.
- 2Press Enroll on your dashboard. An email to us opens with your details: just send it.
- 3We reply by email to complete your enrollment.
- 4Once approved, your classroom unlocks on your dashboard.
FAQ
Where do classes happen?
Live on Discord, Monday to Friday, 8–10 PM IST. You get the invite once you are enrolled.
What if I miss a class?
Every class is recorded and added to your classroom afterwards.
Do classes run on holidays?
Yes. Classes run every weekday from 2 November to 31 December, festivals included.
What do I need?
A laptop that can run Kali Linux (8 GB RAM recommended), a stable internet connection and about 2 hours each weekday evening.
How long do I keep access?
Materials and recordings stay available to you for life.
Is a job guaranteed?
No. You get career preparation and referrals within my network when you are ready, but no job guarantee.
Ready to start?
Classes begin Mon, 2 Nov 2026. Seats are limited to 20.
This batch is full.
Contact about the next batch